▲ “생성형 AI 무기화된 사이버 공격”… 금융권 연쇄 침투부터 로컬 LLM 해킹까지 전방위 위협 (공식 보도 자료)
📌 핵심 브리핑 · 주요 쟁점 및 핵심 요약
생성형 AI가 무기화된 사이버 공격이 현실화되면서 국가 안보와 금융 인프라 전반을 뒤흔드는 초유의 위기가 도래했습니다. 국내 대형 시중은행에서 촉발된 개인정보 유출 사태가 저축은행, 카드사, 증권사, 보험사 등 전 금융권으로 확산된 가운데, 공격 배후에서 초거대 AI 모델과 자동화 침투 테스팅 도구가 결합된 정황이 확인되었습니다. 특히 온라인 디지털 신분증 역할을 하는 '본인확인 연계정보(CI)'와 정밀 대출 잔액까지 유출되어 비대면 대출을 노린 2차 금융 범죄가 우려되는 실정입니다. 외부 통신을 차단한 로컬 LLM과 RAG 기반 북한 해킹조직의 위협, MS 디지털 방어 보고서 2026 분석, 그리고 2.1만 건의 통화 데이터를 개방해 온디바이스 AI로 맞서는 민관 합동 방어 대책을 심층 진단합니다.
대한민국 금융 생태계가 사상 초유의 복합 지능형 사이버 침투에 노출되었습니다. 금융당국과 보안 업계의 조사에 따르면, 이번 금융권 연쇄 해킹 사태는 상대적으로 보안 관리가 취약했던 외주 협력사와 대외 서비스 접점을 자동 탐지하는 인공지능 알고리즘에 의해 촉발되었습니다. 해커들은 기업 내부 모의해킹용으로 개발된 최신 침투 테스팅 도구와 딥시크(DeepSeek) 등 글로벌 생성형 AI 모델을 결합하여, 과거 수개월이 걸리던 시스템 취약점 탐색과 익스플로잇 코드 생성을 단 몇 시간 만에 기계적으로 완결했습니다.
더욱 심각한 위협은 유출된 데이터의 질적 위험성입니다. 예가람저축은행(4만여 명), 신한은행(2만 5,000여 명), KB국민은행 및 주요 증권·카드사 전반에서 단순 인적사항을 넘어 온라인 거래 시 본인을 증명하는 핵심 디지털 암호값인 '본인확인 연계정보(CI)'와 정밀 연소득, 대출 잔액 내역이 대거 빠져나갔습니다. CI가 해커의 손에 넘어갈 경우 제3자 명의로 비대면 신용대출을 실행하거나 알뜰폰(대포폰)을 무단 개통하는 등 과거의 단순 스미싱과는 차원이 다른 파괴적인 2차 금융 사기가 발생할 수 있어 금융권 전체에 비상이 걸렸습니다.
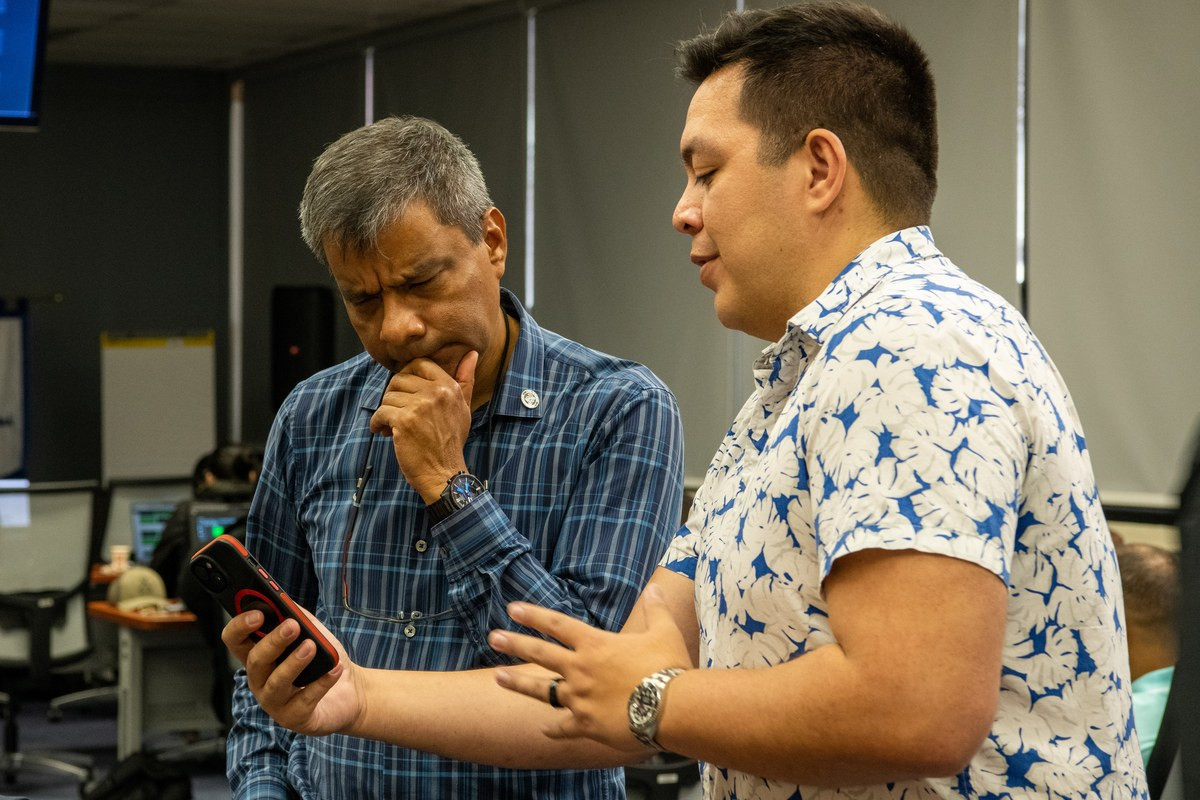
▲ 생성형 AI를 결합한 지능형 침투 공격에 맞서 실시간 모니터링 및 방어 훈련을 진행하는 사이버 보안 작전 현장 (보도 자료)
2. 외부 연동 끊은 '로컬 LLM' 구축: 북한 해킹조직의 AI 무기화와 실시간 악성코드
해커들의 인공지능 활용 전략은 단순히 피싱 이메일 문구를 작성하는 초기 수준을 넘어, 외부 방어망의 추적을 원천 차단하는 독립적인 '폐쇄형 로컬 개발망' 구축으로 고도화되었습니다. 사이버보안 전문기관 지니언스 시큐리티 센터(GSC)의 정밀 분석에 따르면, 북한 정찰총국 산하 해킹조직 김수키(Kimsuky)는 외부 클라우드로 데이터를 전송하지 않는 독립형 로컬 대형언어모델(Ollama, GPT4All 등)과 검색증강생성(RAG) 환경을 구축해 정밀 타깃 공격을 감행하고 있습니다.
공격자들은 탈취한 금융 문서와 연구 자료를 로컬 RAG 데이터베이스에 적재한 뒤, AI 코딩 도구인 커서(Cursor)와 자율형 에이전트 프레임워크를 연동하여 표적 맞춤형 악성 스크립트를 기계적으로 양산하고 있습니다. 이에 더해 중국 오픈소스 코딩 AI의 API와 실시간으로 통신하며 실행 시점마다 고유한 시스템 명령어를 동적으로 조립하는 '레임허그(LAMEHUG)' 악성코드까지 출현했습니다. 이 악성코드는 고정된 바이너리 시그니처가 존재하지 않아 기존 엔드포인트 탐지(EDR) 시스템과 백신 방어선을 완전히 무력화하는 치명성을 보이고 있습니다.
구분 유형
지원 및 적용 대상
환급 및 해결 기준
신청 및 조치 방법
본인확인 연계정보 (CI)
디지털 신분증 핵심 암호값
최고 (치명적)
비대면 신용대출 무단 실행·대포폰 개통
정밀 대출 잔액·연소득
차주별 실제 금융 거래 데이터
높음 (고위험)
실제 잔액 언급하는 '맞춤형 대환대출' 사기
로컬 LLM & RAG 해킹
외부 연동 없는 폐쇄형 AI 개발
최고 (국가 안보)
커서(Cursor) 연동 악성코드 기계적 양산
실시간 명령어 악성코드
알리바바 오픈소스 코딩 API 통신
신종 지능형 위협
고정 시그니처 부재로 백신·EDR 회피
민관 온디바이스 AI 방어
국과수 2.1만 건 통화 데이터 개방
선제적 방어 기술
단말기 내부 실시간 피싱 문맥 탐지 차단
SPONSORED · ADVERTISEMENT
3. MS 디지털 방어 보고서 2026: AI 에이전트 표적 공격과 대화 기록 탈취 급증
글로벌 빅테크 마이크로소프트가 전 세계 보안 데이터를 집대성해 발표한 '2026 디지털 방어 보고서(Microsoft Digital Defense Report 2026)'는 생성형 AI 자체가 새로운 공격 벡터로 자리 잡았음을 명확히 경고합니다. 보고서에 따르면 초기 침투 경로 중 이메일 피싱이 차지하는 비중은 2025년 7%에서 2026년 23%로 3배 이상 폭증했으며, 악성 QR코드를 활용한 '퀴싱(Quishing)' 탐지 건수만 1억 4,500만 건을 돌파했습니다. 특히 공격 표적이 되는 AI 서비스 중 OpenAI 및 애저 서비스(39%)와 기업 맞춤형 AI 에이전트(31%)가 전체의 70%를 차지했습니다.
특히 이용자를 대신해 복잡한 자율 업무를 수행하는 'AI 에이전트'에 대한 공격이 집중되고 있습니다. 마이크로소프트의 프롬프트 정밀 분석 결과, AI 에이전트에게 전달되는 명령 중 기업 내부의 비밀 자격 증명 탈취나 권한 탈취를 노린 악의적 탈옥(Jailbreak) 프롬프트 시도가 전체의 17%에 달했습니다. 나아가 악성 브라우저 확장 프로그램을 몰래 설치시켜 사용자의 ChatGPT 및 DeepSeek 대화창에 입력된 소스 코드와 기업 재무 정보를 해외 서버로 빼돌리는 신종 공급망 공격이 전 세계 90만 건 이상 적발되며 기업 보안의 패러다임 전환을 압박하고 있습니다.
▲ 개인정보 유출 및 본인확인 연계정보(CI) 탈취 사태로 2차 비대면 금융 범죄 예방 비상이 걸린 금융권 빌딩 전경 (보도 자료)
4. 민관 합동 '온디바이스 AI' 방어선과 금융 소비자를 위한 4대 긴급 행동 수칙
생성형 AI로 무장한 초정밀 금융 공격에 맞서 대한민국 정부와 민간 통신·보안 기업들도 실제 데이터를 기반으로 한 방어망 구축에 전격 돌입했습니다. 금융위원회, 과기정통부, 개인정보보호위원회, 국립과학수사연구원, KISA는 긴급 업무협약을 체결하고, 국과수가 보관 중인 2만 1,000여 건의 실제 보이스피싱 통화 음성을 비식별 텍스트로 정밀 가공하여 민간 AI 연구소에 전면 개방했습니다. SK텔레콤 등 이동통신사들은 이 빅데이터를 소형언어모델(sLM)에 미세조정(Fine-tuning)하여, 통화 내용이 외부 서버로 유출되지 않고 스마트폰 내부에서 실시간으로 사기 문맥을 판별하는 '온디바이스 AI' 보안 솔루션을 상용화했습니다.
이와 함께 금융 소비자 개인의 기민한 방어 조치가 반드시 병행되어야 합니다. 첫째, 금융감독원 파인(FINE) 포털에 접속해 비대면 신규 대출과 카드 발급을 사전에 차단하는 '금융거래 안심차단서비스'를 즉시 신청해야 합니다. 둘째, '개인정보노출자 사고예방 시스템'에 본인 계정을 등록하여 본인 확인 절차를 2중 강화합니다. 셋째, 스마트폰 갤러리와 메모장에 저장된 신분증 사진, 보안카드, 계좌 비밀번호 이미지를 영구 삭제해야 합니다. 마지막으로 금융기관과 공공기관은 어떠한 경우에도 피해보상이나 유출 확인을 이유로 문자메시지에 링크(URL)나 QR코드를 첨부하지 않는다는 점을 명심하고 출처 불명의 링크 접속을 절대 차단해야 합니다.
“Generative AI Weaponized in Cyber Warfare”: From Financial Breaches to Local LLM Exploits, Threats Multiply
Generative AI has been decisively weaponized across international cyber warfare, precipitating unprecedented systemic risks across financial infrastructures and national security systems. Following cascading customer data breaches across South Korean commercial banks, savings institutions, credit card issuers, and brokerages, forensic disclosures confirm that threat actors combined frontier language models with automated penetration testing frameworks. Beyond credential harvesting, the compromise of connecting information (CI)—the digital identity anchor for non-face-to-face authentication—exposes citizens to catastrophic secondary loan fraud. This investigative report evaluates isolated local LLM and RAG weaponization by state-sponsored hacking syndicates, examines Microsoft's Digital Defense Report 2026, and details public-private countermeasures deploying on-device AI trained on 21,000 voice fraud records.
📌 Key Takeaways
Financial Infrastructure Infiltration and CI Compromise: Customer records and Connecting Information (CI) exfiltrated across banking and savings institutions, elevating synthetic loan fraud risks.
Isolated Local LLM and Dynamic Malware Weaponization: State-sponsored syndicates leverage air-gapped LLMs and Cursor suites, while LAMEHUG malware queries coding APIs to evade EDR signatures.
Public-Private On-Device Defenses: 21,000 forensic voice fraud transcripts declassified to train private on-device SLMs, paired with four consumer pre-emptive credit freeze protocols.
1. The Nexus of Generative AI and Exploitation Frameworks: Cascading Breaches and CI Theft
South Korea's financial infrastructure confronts an unprecedented vector of synthetic cyber warfare. Forensic analyses conducted by financial supervisory bodies reveal that cascading breaches across the banking and non-banking sectors were catalyzed by algorithmic scanners mapping vulnerabilities across third-party contractors and external API interfaces. Adversaries weaponized commercial penetration testing suites alongside frontier generative models including DeepSeek, automating the synthesis of zero-day exploits within hours—a phase that historically required months of reconnaissance.
The severity of the incident is compounded by the compromise of Connecting Information (CI)—the cryptographic cornerstone governing digital identity and non-face-to-face verification across South Korean institutions. Breaches across Yegarim Savings Bank (over 40,000 accounts), Shinhan Bank (25,000 accounts), and major card issuers exposed not merely personal identifiers, but granular debt balances, credit limits, and CI tokens. With CI compromised, malicious syndicates can execute unauthorized non-face-to-face credit loans and fraudulently provision mobile accounts, escalating secondary extortion risks far beyond conventional smishing.
▲ Official Press Archive & Contextual Documentation
2. Air-Gapped Local LLM Weaponization: State-Sponsored Syndicates and Dynamic Payloads
Adversarial tradecraft has rapidly evolved from drafting rudimentary phishing lures toward constructing isolated, air-gapped development infrastructure designed to evade cloud monitoring. Technical intelligence from the Genians Security Center (GSC) confirms that Kimsuky—a cyber reconnaissance unit subordinated to North Korea's Reconnaissance General Bureau—engineered operational environments utilizing offline local LLMs (such as Ollama and GPT4All) integrated with Retrieval-Augmented Generation (RAG).
Adversaries feed exfiltrated financial data into local RAG vector databases, linking them with developer tools like Cursor and autonomous agent frameworks to generate targeted spear-phishing payloads at machine speed. Concurrently, novel malware strains such as LAMEHUG directly query external open-source coding APIs to dynamically synthesize operating system commands at execution time. Devoid of persistent static byte sequences, these dynamic payloads bypass signature-based Endpoint Detection and Response (EDR) agents with near-total operational stealth.
Category
Target Scope
Standard / Benefit
Procedure / Action
Identity Verification Linked Information (CI)
Core Encryption Value of Digital ID
Critical (Fatal)
Unauthorized Execution of Non-Face-to-Face Credit Loans and SIM Card Activation for Fraudulent Phones
Precise Loan Balances and Annual Income
Actual Financial Transaction Data by Borrower
High (High Risk)
Fraud Involving 'Customized Refinancing Loans' Mentioning Actual Balances
Local LLM & RAG Hacking
Development of Closed AI Without External Integration
Critical (National Security)
Mechanical Production of Cursor-Linked Malware
Real-Time Command Malware
Alibaba Open Source Coding API Communication
Emerging Intelligent Threats
Evading Antivirus and EDR Due to Absence of Fixed Signatures
Public-Private On-Device AI Defense
National Forensic Service Opens 21,000 Call Data
Proactive Defense Technology
Real-Time Phishing Context Detection and Blocking on Devices
3. Microsoft Digital Defense Report 2026: Hyper-Targeting AI Agents and Session Harvesting
Microsoft's flagship Digital Defense Report 2026 underscores that generative artificial intelligence has become both a tactical multiplier and a primary attack surface. Phishing vectors accounted for 23 percent of initial access compromises in 2026—tripling from 7 percent in 2025—while QR code phishing (quishing) surpassed 145 million enterprise detections. Commercial generative platforms accounted for 70 percent of targeted AI assets, dominated by Azure OpenAI instances (39%) and proprietary enterprise AI agents (31%).
Vulnerabilities surrounding autonomous AI agents represent an acute operational crisis. Deep telemetry reveals that 17 percent of malicious prompts processed by enterprise agents seek unauthorized session hijacking or confidential memory exfiltration. Furthermore, malicious browser extensions designed to covertly harvest ChatGPT and DeepSeek session histories affected over 900,000 enterprise endpoints globally, silently siphoning proprietary source code, internal network architecture diagrams, and high-privilege credentials stored within active chat logs.
▲ Institutional Field Data & Media Archive
4. Public-Private On-Device AI Defenses and Four Mandatory Consumer Safeguards
To counter AI-augmented threat actors, the South Korean government and private telecommunications providers have deployed defensive architectures anchored in empirical operational data. The Financial Services Commission, National Forensic Service, and KISA ratified an inter-agency memorandum declassifying 21,000 verified voice fraud audio transcripts, anonymizing them into structured datasets for private machine learning laboratories. Major telecommunications operators, including SK Telecom, deployed fine-tuned small language models (sLM) directly onto mobile hardware, enabling on-device contextual fraud detection that intercepts extortion attempts locally without cloud latency or privacy leakage.
Simultaneously, financial consumers must rigorously enforce four immediate defensive protocols. First, citizens should register for the Financial Transaction Pre-Emptive Blocking Service via the FSS FINE portal to legally freeze non-face-to-face loan and card issuances. Second, individuals should enroll in the Identity Exposure Accident Prevention Registry to mandate rigorous multi-factor authentication across all transactions. Third, all stored photographs of national ID cards, security code cards, and account credentials must be permanently eradicated from smartphone galleries. Finally, users must permanently avoid clicking hyperlinks embedded in unsolicited SMS messages, as public agencies never distribute compensation or breach lookup tools via public URLs.
Recommended Deep-Dive Investigations TOP 3
GLOBAL REPORT
Computer Programmer who love programming.
Computer Programmer Who love Riding Bicycle.
Computer Programmer who love trip in abroad.
Computer Programmer who love studying about programming
- even if sometimes it's very boring.
Computer Programmer who love talking with person.
- I love communication with person.
1월이 시작되면 감기는 이미 우리 곁에 와 있습니다. 2월, 3월, 4월까지 이어지는 추위와 건조함은 코와 목을 가장 먼저 공격합니다. 아침에 일어나자마자 막혀 있는 코. 계속 흐르는 콧물. 괜히 칼칼해지는 목. 이 증상은 “시작”일 뿐입니다. 한 번 무너지면 일주일, 길면 한 달까지 끌고 갑니다. 약을 먹으면 잠깐 괜찮아집니다. 하지만 며칠 뒤 또 반복됩니다. 왜일까요? 감기는 ‘치료’의 문제가 아니라 ‘관리’의 문제이기 때문입니다. 대부분은 감기가 오고 나서 약을 찾습니다. 하지만 진짜 중요한 건 감기가 오기 전에 코와 목을 지키는 것입니다. 건조한 실내 공기, 차가운 바깥 공기, 눈에 보이지 않는 세균. 코와 목은 매일 공격받고 있습니다. 지긋지긋하죠! 그런데도 우리는 아무 준비 없이 버티고 있습니다. 이번 겨울도 그렇게 보낼 건가요? 사실 방법은 어렵지 않습니다. 코를 깨끗하게 관리하고, 목을 따뜻하게 보호하고, 점막을 촉촉하게 유지하고, 기관지를 미리 관리하고, 외부 공기를 차단하는 것. 이 다섯 가지만 꾸준히 해도 감기약 없이 겨울을 보내는 것이 충분히 가능합니다. 🔥 이제부터 그 방법을 하나씩 살펴보겠습니다. 🔥 1. 코와 목을 먼저 관리해야 하는 과학적 이유 감기의 대부분은 코 점막에서 시작됩니다. 국제 학술지 Nature Reviews Microbiology 와 Journal of Allergy and Clinical Immunology 에 실린 호흡기 감염 관련 연구들에서는, 감기 바이러스가 비강 상피세포에 먼저 부착해 증식한다는 점을 설명하고 ...
리모델링사업이 진행 중인 아파트를 매매할 때 “계약금 10%를 언제까지 내야 하느냐”는 질문이 특히 많이 나옵니다. 이주공고(이주 안내)가 7~11월쯤이라고 들으면, 그 시점에 맞춰 계약금도 움직일 것 같아서 더 헷갈리기 쉽습니다. 하지만 실제 납부기한은 ‘이주공고가 언제냐’만으로 자동 결정되지 않는 경우가 많습니다. 1) 계약금 10% 납부기한: 결국 ‘문서에 적힌 일정’이 기준 계약금 10%를 언제까지 납부해야 하는지는, 내가 서명하는 매매계약서(특약 포함) 와 사업주체/조합이 제시한 공고·안내문 에 적힌 납부 일정이 기준이 됩니다. 실제 공고문에서는 분양대금 납부의 큰 틀(계약금→중도금→잔금)을 먼저 안내하고, 상세 일정은 별도 표나 유의사항으로 제시하는 방식이 흔합니다. 또, 계약서 문구에 따라 지급 시점이 조건부로 설정될 수도 있습니다. 예를 들어 한 사례 소개 자료에서는 용역계약서에 잔금(10%) 지급시기가 “사업승인 후”로 기재되어 있었다는 점이 언급됩니다. 이런 식으로 ‘사업 단계’와 지급을 연동하는 문구가 들어가면, 질문의 답은 계약서 문구를 확인해야만 확정됩니다. 관련 내용은 링크 에서 문구 사례를 확인할 수 있습니다. 2) 입주자모집공고에서 확인되는 ‘납부 순서’와 잔금 마감 시점 공고문에 적힌 문구를 보면, 납부 순서와 잔금 마감에 대한 기준이 비교적 명확하게 제시되는 경우가 있습니다. 예를 들어 한 입주자모집공고에는 “분양금액(주택가격)은 계약금, 중도금, 잔금의 순서로 납부”하며 “잔금은 입주(열쇠 수령일) 전에 완납”해야 한다고 안내되어 있습니다. (문구 확인: 링크 ) 이 문구가 의미하는 바는 최소 2가지입니다. 분양/공급 형태의 문서에서는 ‘계약금→중도금→잔금’ 흐름이 공식적으로 안내될 수 있습니다. 잔금은 “입주(열쇠 수령)” 이전에 완납해야 한다는 마감 기준이 문서에 적혀 있을 수 있습니다. 다만, 위 공고문 문구는 잔금 마감에 대한 기준을 보여주지만, 계약금 10%의...
윤석열 전 대통령 탄핵 인용 소식을 접하면, 가장 궁금한 지점은 ‘헌재가 정확히 무엇을 위헌·위법으로 봤는가’입니다. 또한 탄핵과 별개로 진행되는 형사재판(내란 우두머리 혐의 등)이 어디까지 왔는지도 함께 정리할 필요가 있습니다. 아래 내용은 제공된 기사/게시물 스니펫과 링크에서 확인되는 범위만 모아, 일반인이 흐름을 이해하기 쉽게 정리한 것입니다. 1) 탄핵 인용 관련: 스니펫에서 확인되는 ‘판단의 골격’ 제공된 근거 중 조국혁신당 사이트에는 헌법재판소가 윤석열 탄핵 심판에서 “피청구인의 위헌·위법행위는 국민 신임 …”이라는 취지로 판단했다는 문장이 인용돼 있습니다( 링크 ). 이 인용문만 놓고 보면, ‘위헌·위법행위’가 있었는지와 그로 인해 ‘국민의 신임’이 어떻게 평가됐는지가 핵심 축으로 소개됩니다. 다만 질문에서 요청하신 세부 항목, 즉 비상계엄 선포 자체를 문제 삼은 구체적 이유, 계엄 이후 조치(포고령, 국회 통제 등)의 어떤 지점이 헌법 위반인지, 국회의 권한행사 방해 및 정치활동 제약을 어떤 논리로 판단했는지 등은, 이번에 제공된 근거의 제목/스니펫만으로는 조항·사실관계·판단 구조가 그대로 제시돼 있지 않습니다. 따라서 이 글에서는 ‘헌재가 무엇을 문제 삼았다’는 세부 리스트를 단정적으로 재구성하기보다, 현재 확인 가능한 문구 수준의 요약(위헌·위법행위 → 국민 신임의 문제로 평가)까지만 적습니다. 만약 헌재 결정문 전문(주문 및 이유)이 추가로 확인되면, 그때는 문장 단위로 ‘어떤 행위’와 ‘어떤 헌법 원리/조항’이 연결되는지(예: 권력분립, 국회의 권한, 정치적 기본권 등) 구조화해 정리하는 것이 가장 정확합니다. 2) 형사 절차(내란 혐의) 관련: 체포영장과 1심 선고 언급 탄핵 심판과 별도로, 12·3 비상계엄 사태로 내란 혐의를 받는 윤석열 대통령에 대해 2024년 12월 31일 체포 영장이 발부됐다는 BBC 보도가 있습니다( 링크 ). 해당 보도는 ‘현직 대통령’에 대한 체포영장 발부라는 점을 함께 언급합니다. 또...




0 댓글